Set Up a Free Consultation
NGCS SOFTLESS · Zero Software Attack Surface

Secure by Design. Secure by Default.

Eliminating software-level vulnerabilities with hardware-driven, SOFTLESS network security solutions for critical industrial infrastructures.

<3μs
AES-256 Latency
0%
SW Attack Surface
100%
Bandwidth Preserved
99.2
Live Gbps Throughput
<3μs
Encryption Latency
ZERO
Software Flaws
SF-106 CYBER CONTROLLER // APEX REV.4
FPGA Core
FW
Crypto
AES
DDoS
MIT
Router
RTR
Monitor
TAP
Health
HLT
99.2
Gbps
1.1μs
Latency
0
SW Flaws
<3μsAES-256 Encryption Latency
100%Bandwidth Preserved
ZEROSoftware Attack Surface
68%Cyberattacks Are Ransomware
9×Real-Time Independent Firewalls (SF-106-8)
15yr+FPGA R&D Behind NGCS Technology
<3μsAES-256 Encryption Latency
100%Bandwidth Preserved
ZEROSoftware Attack Surface
68%Cyberattacks Are Ransomware
9×Real-Time Independent Firewalls (SF-106-8)
15yr+FPGA R&D Behind NGCS Technology
Core Technology

The SOFTLESS
Innovation Stack

Three layers of hardware-native engineering eliminate every software vulnerability vector. Security logic wired directly into silicon — not installed, not patched, not exploited.

01
Step 01 · VHDL Logic
Ethernet Standards in
Wired Logic
Cybersecurity algorithms are written directly in Hardware Description Language (VHDL) — not software. Every Ethernet standard becomes immutable, silicon-level logic that cannot be exploited remotely.
Hardware Description Language · VHDL
02
Step 02 · FPGA Fabric
Agile FPGA
Implementation
VHDL logic is programmed into reconfigurable FPGA components — delivering sub-microsecond latency, scalable performance, and complete immunity from software-layer remote exploits.
Programmable Silicon · <3μs Latency
03
Step 03 · PCB Integration
Integrated Electronic
Board Architecture
The complete SOFTLESS stack is realized on a production electronic board — a resilient physical microchip architecture that is fundamentally resistant to any remote software exploit or supply-chain attack.
Production PCB · Zero Remote Attack Vector
SF-106 Series

Flagship
Product Lineup

Three purpose-built controllers — each a complete SOFTLESS security node. Zero software. Zero compromise. Deployable on DIN rail or PCIe.
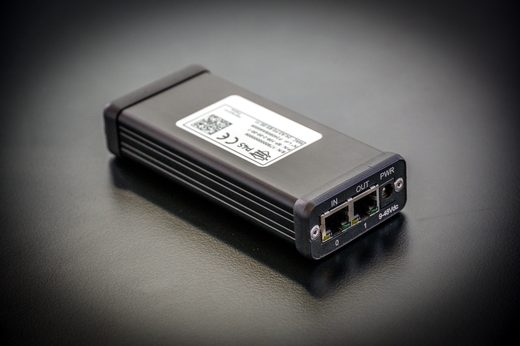
SF-106-2 // CipherWall · 2-Port
NGCS SF-106-2 CipherWall hardware device
2× RJ45 1GbE POE / 9–48V 70×40×20mm
NGCS · SF-106-2 · REF: SF-106-2-WPA / IKEv2
SF-106-2
CipherWall
High-performance hardware cipher and firewall. AES-256-GCM-16 IPSec encryption, real-time DoS/DDoS protection, and native firewall enforced entirely in FPGA logic — deployable on any live network without disruption.
Total Speed (2 ports FD)4 Gbps
Routing Latency (VPN+FW)3μs – 25μs
IPSec Speed (per port)1 Gbps AES-256-GCM-16
Max VPN Tunnels (per port)16
Firewalls / Rules per Port1 FW · 32 Rules
Connectivity2× RJ45 1000BaseT + USB-C
Power Supply+9V–+48V DC or POE
Operating Temp−40°C to +85°C
Dimensions / Weight70×40×20 mm · 170 g
Max Consumption1 W
Total protection against DoS & DDoS — processed in-traffic, pre-OS
AES-256-GCM-16 IPSec encryption · gPTP sync ±10ns/hop
POE pass-through — acts as POE injector at 48V · 1 W max consumption
Inbound rules: flow frequency, MAC, IP, VLAN, protocol/port filtering
TAP-106-8 // Network Probe · 8-Port
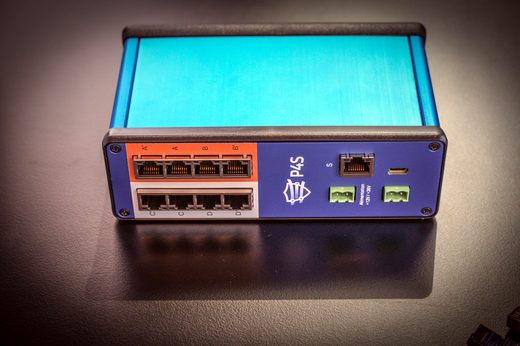
NGCS TAP-106-8 Network Probe hardware device
8× RJ45 1GbE 2× TAPs DIN Rail No Config
NGCS · TAP-106-8 · NETWORK PROBE
TAP-106-8
Network Probe
Real-time passive hardware TAP with 2 fully independent monitoring channels. 100% replication of outbound traffic on ports A', B' and C', D' — zero disruption, zero packet loss, zero added latency, no configuration required.
Max Throughput per TAP2 Gbps (2×1 full duplex)
Replication per Port (A'/B'/C'/D')1 Gbps
Independent TAPs2 (fully independent)
Copper Interfaces8× RJ45 1000BaseT
Power Supplies2× redundant
Power Supply+12V to +36V DC
Operating Temp−40°C to +85°C
Dimensions / Weight165×100×65 mm · 780 g
Max Consumption6 W
Packet Loss / Added LatencyZERO / ZERO
100% passive inline TAP — zero disruption to live infrastructure
Protection diode prevents any upstream data flow contamination
No configuration required — plug-in DIN rail deployment
Industrial grade: −40°C to +85°C · gPTP · redundant PSU
SF-106-8 // Network Controller · 9-Port
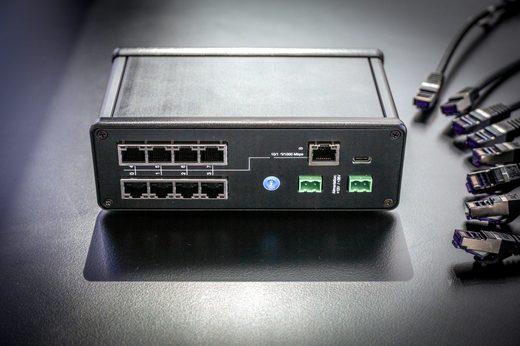
NGCS SF-106-8 Cyber Network Controller device
9× RJ45 1GbE 9 Real-Time FW DIN Rail
NGCS · SF-106-8 · REF: SF-106-8-WPA / IKEv2
SF-106-8 Cyber
Network Controller
The ultimate industrial cyber network controller — 9 independent real-time hardware firewalls (1 per port), AES-256-GCM-16 IPSec, data flow monitoring, health telemetry, and intelligent routing. Commuter, router, cipher, and security node in a single SOFTLESS appliance.
Total Speed (9 ports FD)18 Gbps
Routing Latency (VPN+FW)3μs – 25μs
IPSec Speed (per port)1 Gbps AES-256-GCM-16
Max VPN Tunnels (per port)32
Firewalls / Rules per Port9 FW · 64 Rules
Connectivity9× RJ45 1000BaseT + USB-C
Power Supply+12V–+36V DC · Redundant
Operating Temp−40°C to +85°C
Dimensions / Weight165×100×65 mm · 780 g
Max Consumption10 W
9 fully independent real-time firewalls — 1 per port, ultra-low latency
Health monitoring: anomaly detection, timestamping, CISO & AI transmission
DIN rail · redundant PSU · gPTP sync ±10ns/hop · seamless installation
Rules: flow frequency/consistency, MAC, IP, QinQ/VLAN, protocol/port
Industry Impact

The Painful Reality of
Software Vulnerabilities

Software-layer security fails at scale. New Gen eliminates the attack surface entirely — not by patching vulnerabilities, but by removing the software layer that creates them.

0%
Ransomware Prevalence
of organizations worldwide were hit by a ransomware attack in the past year — the single most prevalent threat facing every critical industry sector in 2026.
0
Software Flaws on
New Gen Hardware
No software layer means no software vulnerabilities. NGCS SOFTLESS delivers mathematically zero software-exploitable attack surface — not reduced, eliminated.
<0μs
64-Byte Frame
Encryption Latency
AES-256-GCM hardware encryption executes in under 3 microseconds for a 64-byte frame — over 1,000× faster than any software cryptography stack.
Software Security Reality
Patches, updates, zero-days.
Perpetual vulnerability cycle.
vs.
New Gen Approach
NGCS SOFTLESS Reality
No software. No patches.
No attack surface.
Services & Sectors

Mission-Critical
Domain Expertise

NGCS SOFTLESS is purpose-built for environments where downtime is measured in catastrophe. Specialized deployments for the world's most sensitive infrastructure.

Trusted Sectors
Energy & Power Grid
Critical national energy infrastructure — OT/ICS networks demanding zero-downtime protection with full bandwidth preservation.
Oil, Gas & Petrochemical
Remote pipeline SCADA and refinery networks secured with hardware-native security appliances — no software attack surface.
Medical & Healthcare
Hospital networks and medical device infrastructure protected against ransomware — the #1 threat to healthcare globally.
Large Administrations
Government, defence, and municipal networks requiring sovereign, independently verifiable hardware security architecture.
Specialized Services
01
Cybersecurity Risk Analysis
End-to-end assessment of your network environment — identifying attack surfaces, mapping vulnerabilities, and delivering an actionable remediation roadmap built around NGCS SOFTLESS architecture.
02
Industrial Network Design
Specialized OT/ICS network architecture for energy, oil & gas, and manufacturing — designed from the ground up for hardware-native security, reliability, and zero-downtime operations.
03
Cyber Network Visualization
Real-time visual intelligence of your entire network topology — traffic flow, anomaly detection, and hardware health status displayed through TAP-106-8 monitoring architecture.
04
Deployment & Integration
Expert hardware deployment with zero disruption to live operations — full integration support, firmware lifecycle management, and ongoing mission-critical infrastructure partnership.
Ready to Eliminate
Your Software Attack Surface?
Join critical infrastructure operators worldwide deploying NGCS SOFTLESS hardware security. Our engineers analyze your environment and design a deployment with zero operational disruption.
Set Up a Free Consultation Contact Our Team
About New Gen Cyber Solutions

Pure Simplicity.
Absolute Security.

New Gen Cyber Solutions was founded on a single conviction: software-based cybersecurity is structurally broken. As long as security depends on software, it inherits every vulnerability that software carries.

After 15+ years of R&D in programmable logic hardware, our team engineered NGCS SOFTLESS — a breakthrough architecture that writes security directly into FPGA silicon. No OS. No drivers. No exploitable code surface. Security that exists before software boots, operates independent of it, and cannot be removed by it.

Hardware engineered in partnership with P4S, France.

15+
Years of R&D
0
SW Attack Surface
<3μs
AES-256 Latency
Learn More About Us Contact Our Team →
01
15+ Years of FPGA Security R&D
Our technology emerges from over a decade and a half of research in real-time data processing using exclusively programmable logic hardware — not adapted from general-purpose computing, purpose-built for security.
02
Sovereign Hardware Engineering
End-to-end French sovereignty — R&D, PCB design, manufacturing, and technical support. Our supply chain is controlled, auditable, and free from third-party hardware backdoor risk.
03
Low CSR Footprint
NGCS devices consume as little as 1W at full operation. Minimal carbon footprint, maximum security density. Industrial-grade hardware built to last in the harshest environments: −40°C to +85°C.
04
Easy Deployment, No Disruption
Drop-in installation at any point in a live network — no software to install, no configuration agent, no maintenance window. NGCS appliances integrate transparently via full IEEE 802 Ethernet compliance.